
CI/CD RISK AND AUDIT
Your CI/CD pipeline is now an attack path. Is it in your audit scope?
AI agents change code and pipeline configuration using your engineers' credentials, so security tools see an authorized user. CloudBees CI brings Jenkins controllers under central access control, audit logging, and a vetted plugin baseline, without a migration.


AI agents are now privileged users in your pipelines
AI agents work in seconds, authenticate as your engineers, and modify the configuration that governs everything else. Across a fragmented Jenkins environment with no central inventory, that activity looks legitimate, so no control fires.
- Govern your connected Jenkins controllers from one control point
- Enforce least-privilege access for engineers, service accounts, and AI agents
- Keep centralized build audit logs for quick handoff
- Hold every controller to an approved configuration baseline
- Reduce third-party risk with a curated, tested plugin set
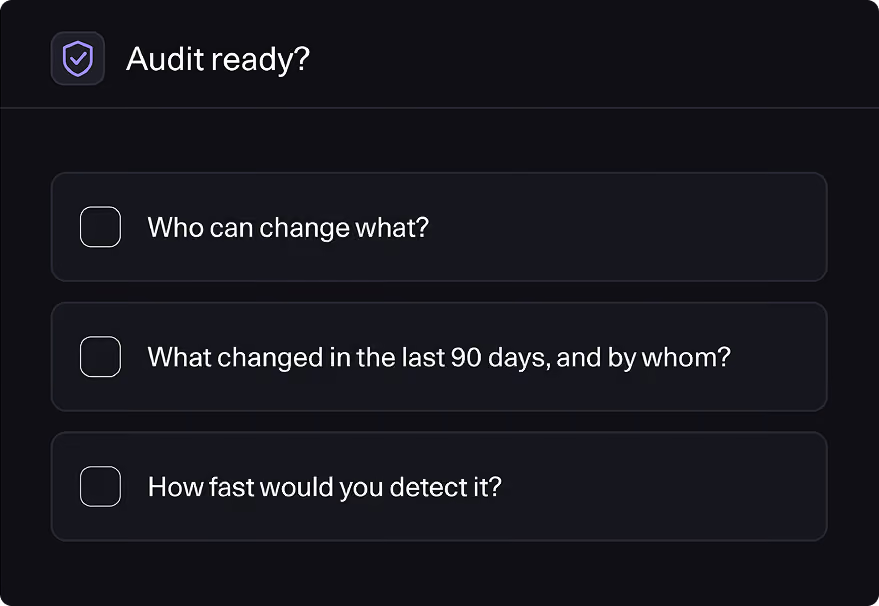
Could you answer these questions for your auditors?
Who has permissions to make changes in your CI? Can you tell you who made what changes and when? Map your gaps in a session with us.
Controls that bring Jenkins into your security program
Writing code is no longer the bottleneck. Governing it is. CloudBees CI adds enterprise controls over the Jenkins you already run.

One view of every connected controller
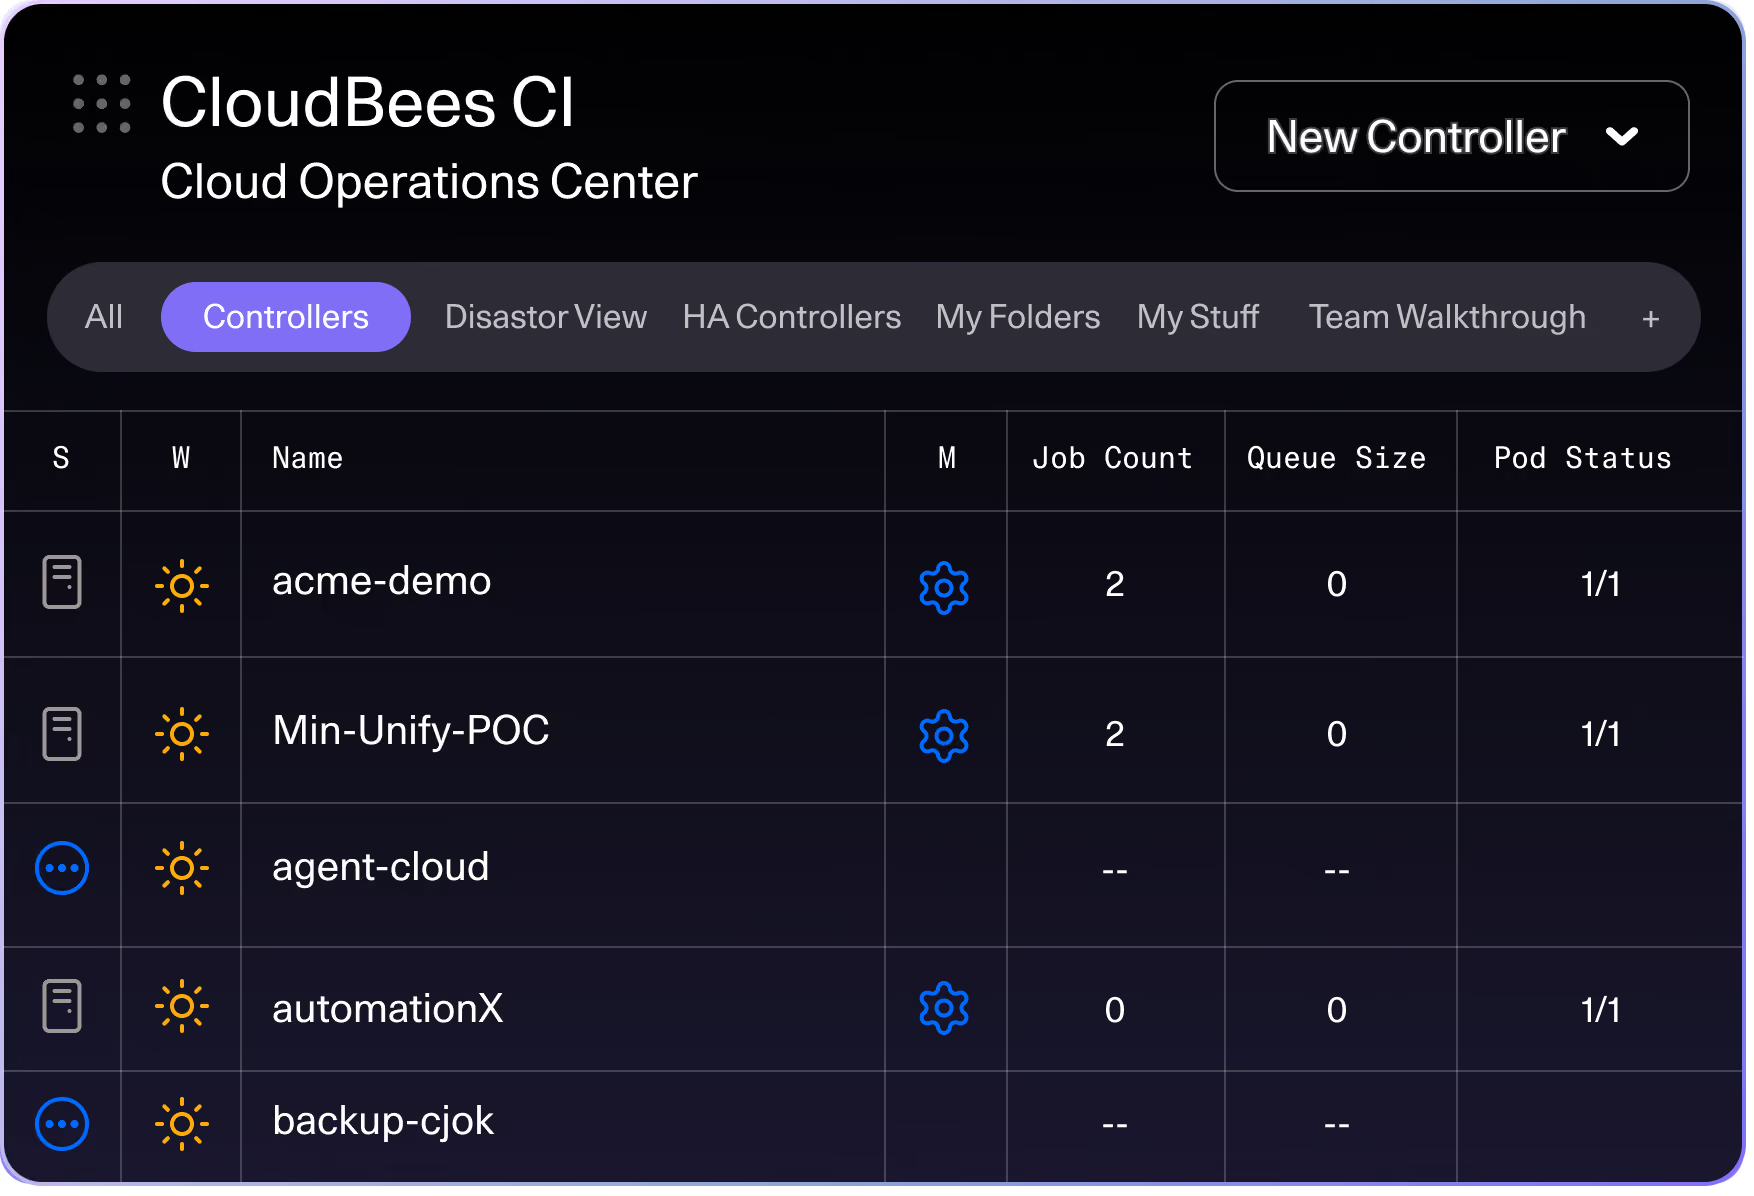
You can't secure what you can't see. Operations Center is a single view of every connected Jenkins controller, with centralized plugin vetting and performance monitoring.

Least-privilege access, with an audit trail
Centrally managed, role-based access with predefined templates limits who can change pipelines. When AI agents act with an engineer's credentials, tight role scoping limits them too. Audit logs record the changes.

A configuration baseline in code
Configuration as Code defines every controller in declarative YAML, so each one is built from the same approved configuration instead of one-off settings.

Lower third-party plugin risk
Plugins are a large and often unmanaged part of your attack surface. The CloudBees Assurance Program provides a curated, tested plugin set, with automated updates through Beekeeper.

Trace what happened in any pipeline run
Pipeline Explorer and real-time monitoring surface logs, metrics, and pipeline detail across environments, so your team can see what ran and where it failed.
The risk has moved into the build layer
The consequence
81%
More production incidents from AI code
The exposure
61%
Of enterprise codebases are AI-assisted
Time to detect
7 days
Credentials exposed before detection
Trusted by enterprises, loved by developers

Acquia brings 16+ Jenkins instances under centralized, compl
Inconsistent security across 16+ Jenkins instances raised FedRAMP concerns. Consolidating on CloudBees CI gave Acquia centralized management and governed CI/CD that meets compliance requirements.

Autodesk gets SOC 2 without the burden
With 4,000 engineers and more than 200 applications, Autodesk runs CloudBees CI and meets SOC 2 without the compliance burden.
Salesforce migrates DevOps to the cloud with CloudBees CI
Salesforce moved software development to CloudBees CI on Amazon EKS, improving productivity, security, and supporting the continuous delivery of innovative solutions on the Salesforce platform.
CloudBees CI vs. Open-source Jenkins
Why security teams choose CloudBees CI
Proof when the auditors ask
Pull who changed what from centralized logs, instead of reconstructing it controller by controller before every audit.
Risk reduction without a migration project
Jenkins and your pipelines stay in place, so you reduce exposure now instead of waiting on a multi-year replatform.
Controls that keep pace with AI
Access, configuration, and plugin controls are set centrally and apply to every controller, so coverage doesn't depend on each team keeping up with AI-driven change.
Built for regulated environments
Native workflow support for SOC 2, PCI, FedRAMP, and ISO 27001.
Securing the software factory in the age of AI agents

Your board asked for proof. We're here to help.
We can help you identify the risk that's living in your CI/CD and build a roadmap to tighten control where it matters most.